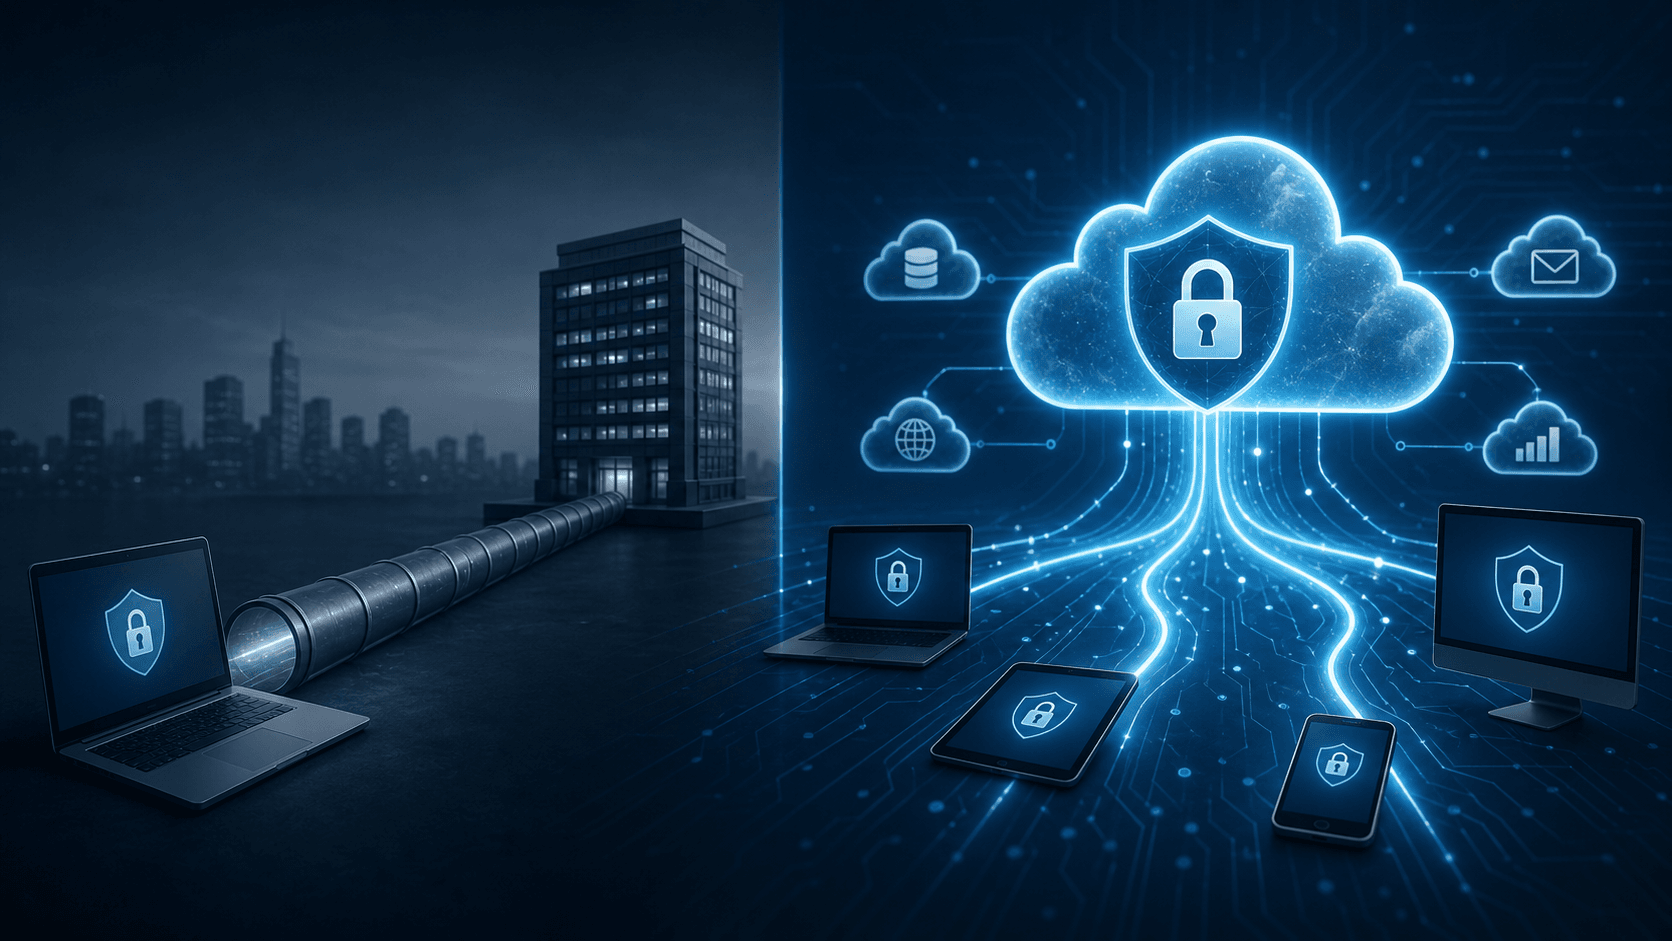
The VPN vs SASE question is one every business owner running a remote or hybrid workforce should be asking right now, because the tool most companies still rely on for secure access was designed for a world that no longer exists. A traditional VPN was built to connect a remote worker back to an office network. Today your applications live in the cloud, your staff work from anywhere, and the threats are far more sophisticated. This post breaks down the real differences between VPN and SASE, what those differences mean for your team day to day, and how the two platforms we deploy, Timus SASE and Perimeter 81, compare.
What a VPN Actually Does, and Where It Falls Short
A VPN, or virtual private network, creates an encrypted tunnel between a user’s device and your corporate network. Once that tunnel is up, the user is effectively inside the network. This is the classic castle-and-moat model: build a strong wall, and trust everyone who makes it past the gate.
That model carries real problems in a modern environment.
- Implicit trust is dangerous. Once a user or device is connected, the VPN generally grants broad access to the internal network. If a laptop is compromised or a credential is stolen, an attacker inherits that same broad access and can move laterally across your systems.
- It backhauls traffic. Most VPNs route all traffic back through a central gateway or data center before sending it out to cloud apps. That detour adds latency and slows everything down, especially for cloud and SaaS tools your team uses all day.
- It does not check device health. A standard VPN verifies the connection at login and then largely stops paying attention. It does not continuously confirm that the device is patched, encrypted, or free of malware.
- It scales poorly. VPN concentrators and firewall appliances have capacity limits. Growth, acquisitions, and remote-work spikes force expensive hardware upgrades.
- Users work around it. Because VPNs are slow and require manual connection, employees disable them, which quietly erases the protection you paid for.
What SASE Does Differently
SASE, which stands for Secure Access Service Edge, is a cloud-delivered model that converges networking and security into a single service. Instead of routing everyone back to a central choke point, SASE inspects and secures traffic at the edge, close to the user, and connects them directly to the resources they need. It bundles capabilities that used to require separate products, including Zero Trust Network Access (ZTNA), a secure web gateway, firewall as a service, and DNS filtering.
The defining principle is zero trust: never trust, always verify. Rather than granting access to the whole network, SASE grants least-privilege access to specific applications, and it verifies identity, device posture, and risk continuously, not just once at login. Access decisions adapt in real time. If a device falls out of compliance or a login looks risky, the platform can require step-up authentication or block the session outright.
VPN vs SASE in Day-to-Day Operations
The technical differences matter, but what business owners really feel is the daily experience. Here is how VPN vs SASE plays out in practice.
For the user. With a legacy VPN, the employee has to remember to connect, wait through a sluggish tunnel, and accept that everything from email to video calls feels slower because it is routing through headquarters. Drops mean reconnecting and lost work. With SASE, secure access is always on and invisible. The employee simply works, and traffic takes the fastest path to the nearest cloud point of presence and out to the application. Cloud apps feel fast, protection is automatic, and there is no toggle to forget.
For security and IT. With a VPN, IT sees a connection and little else, and a single compromised endpoint can expose the internal network. With SASE, IT gets continuous visibility into who is accessing what, from which device, and at what risk level. Access is scoped to individual applications, so a compromised account cannot roam freely. Policies are managed from one cloud console instead of a rack of appliances, and audit-ready reporting supports frameworks like HIPAA, SOC 2, and GDPR.
For the business. A VPN is a cost center that grows with hardware and rarely improves the employee experience. SASE consolidates several tools into one subscription, reduces the attack surface, cuts help desk tickets tied to connection problems, and scales without new equipment. It turns secure access from a daily friction point into something the team never has to think about.
Why Business Owners on a VPN Should Ask About SASE
If your company is still running on a VPN, here is why raising the SASE question with your IT provider is worth your time.
- Your security model is outdated. Implicit trust and flat network access are exactly what ransomware operators exploit. Zero trust dramatically shrinks what an attacker can reach.
- Cyber insurance is changing. Insurers increasingly expect zero trust controls and continuous verification. Moving toward SASE can help you qualify for coverage and better rates.
- Productivity is leaking. Every slow VPN session and every workaround is lost time and added risk. Always-on secure access removes both.
- You are paying for tool sprawl. Separate VPN, firewall, web filtering, and DNS products cost more and are harder to manage than one converged platform.
- Your workforce is distributed. VPNs were never designed for a cloud-first, work-from-anywhere reality. SASE was.
The shift is well underway across the industry, and the practical takeaway is simple: if secure access still depends on a VPN, it is time to evaluate what SASE would change for your business.
Timus SASE vs Perimeter 81: Two Platforms We Trust
We deploy two SASE platforms depending on the client, and both replace the legacy VPN with a modern zero trust model. One quick note for clarity: Perimeter 81 was acquired by Check Point and is now branded Check Point Harmony SASE, so you may see it under either name.
Timus SASE
Timus is a 100 percent cloud-native SASE platform built with the small and mid-sized business in mind, and it is the one we most often recommend for lean teams that want strong security without heavy overhead.
- Adaptive zero trust. Timus continuously evaluates user behavior, risk, and device posture instead of making a single decision at login, and layers adaptive MFA on top.
- Always-on secure access. Connectivity is seamless and requires no action from the user, which means the protection actually stays on.
- Fast deployment. Timus can be stood up quickly, often in well under an hour, which keeps rollout disruption low.
- Tight application control. Features like IP-based restrictions let us lock down SaaS applications so they are only reachable through the secure network.
- Converged toolset. VPN replacement, ZTNA, secure web gateway, cloud firewall, DNS filtering, and device posture checks come under one platform, and it integrates with endpoint tools to feed real signals into access policies.
We like Timus because it delivers enterprise-grade zero trust in a package a growing business can actually adopt and manage, and it consistently reduces both attack surface and support tickets.
Perimeter 81, now Check Point Harmony SASE
Perimeter 81, now part of Check Point as Harmony SASE, is a mature, cloud-native SASE platform that converges networking and security and is backed by one of the largest names in cybersecurity.
- Converged security stack. It brings ZTNA, firewall as a service, and a secure web gateway together in one cloud service, with data loss prevention capabilities layered in.
- Global performance. A worldwide network of points of presence keeps connections fast and low-latency for remote users and branch offices.
- Threat intelligence backing. Integration with Check Point’s broader threat intelligence ecosystem adds enterprise-grade protection and centralized management.
- Strong fit for multi-site. It is well suited to connecting branch offices and replacing legacy hardware firewalls and VPNs across multiple locations.
We like Harmony SASE when a client wants the weight of a major security vendor behind their platform, a strong global network, and a converged stack that scales cleanly into the mid-market.
The Bottom Line
The VPN vs SASE decision comes down to whether your secure access model matches how your business actually works. A VPN protects a network perimeter that has largely dissolved, while SASE secures users, devices, and applications wherever they are, with continuous verification and a far smaller attack surface. For most companies running a remote or hybrid team, SASE is not just an upgrade, it is the model secure access is moving to.
At SFV Cloud, we design and manage SASE deployments on Timus and Perimeter 81 (Harmony SASE) for businesses ready to retire the legacy VPN. If you want to know what SASE would mean for your security, your compliance posture, and your team’s daily experience, contact SFV Cloud for an assessment and a migration plan built around how your business operates.